
- Yes, cloud SCADA can be secure, and so can an on-premise system. What decides it is how many pathways reach your control system.
- Every US water system attack with a confirmed cause traces back to on-premise equipment that could be reached from the internet, not to a hosted platform.
- No federal rule and no state drinking water agency prohibits hosted SCADA. That belief traces to a withdrawn EPA memo and to guidance about internet exposure, which is not the same thing.
Spend two days at a rural water conference and you’ll hear the same question at every booth, in most hallway conversations, and usually twice over lunch. Someone leans in and asks whether cloud SCADA is actually secure.
It’s a fair question, and it comes up far more than it did a year ago. Over one weekend in late July 2026, more than 30 Minnesota community water systems were targeted in what the state called a coordinated cyberattack. In Braham, the plant went offline and residents were asked to go easy on the tower supply.
If you want the architecture side of this, there’s a separate brief on our site that walks through it in detail. What I want to do here is take on the two things I hear repeated at every conference that turn out not to hold up: what the attacks we keep hearing about actually had in common, and what regulators have supposedly said about hosted systems. Then I’ll give you the questions I’d want answered about my own plant.
What Actually Went Wrong in the Attacks You’ve Heard About
A few incidents come up in every conversation I have about this. In every case where investigators have actually said how the attackers got in, it wasn’t a hosted platform that got broken into. It was equipment on the plant floor that could be reached from the outside, with a password as the only thing standing in the way.
Aliquippa and Muleshoe: Weak Passwords on Systems Anyone Could Find
In November 2023, the water authority in Aliquippa, Pennsylvania lost control of a booster station. Operators switched to manual and nobody lost service. According to CISA’s alert on the Aliquippa incident, the attackers likely got in by exploiting “poor password security and exposure to the internet.”
No zero-day. Somebody scanned for that port, found the device, and typed four ones.
Two months later, four small Texas towns got hit much the same way. In Muleshoe, attackers guessed their way into the remote login for the tank software, changed settings, and the tank overflowed for 30 to 45 minutes before anyone noticed.
Minnesota: What We Know, and What We Don’t
In late July 2026, more than 30 Minnesota community water systems were targeted over one weekend. Plymouth had equipment affected at two water towers and several lift stations. Braham’s plant went offline.
I want to be careful here. That investigation is still open. Nobody has officially confirmed how the attackers got in, and there’s no confirmed attribution yet. If you’ve read that this was definitely exposed controllers, that’s a reasonable guess, not a finding.
What we do know is what the agencies said that week. The FBI described attackers reaching internet-facing devices and then changing IP addresses and passwords, leaving operators without monitoring or control. CISA’s acting director told utilities to remove publicly exposed PLCs and other control equipment from the internet as soon as possible.
Oldsmar: the Story That Didn’t Hold Up
Now the one I have to correct, because it comes up more than any of them.
In 2021, a plant in Oldsmar, Florida was reported to have had someone remotely raise a chemical dose to a dangerous level. Two years later, the city’s former manager, Al Braithwaite, told a panel that “The FBI conclusion was it didn’t happen.” The FBI’s Tampa office said it couldn’t confirm a targeted intrusion. Operator error, most likely.
I bring it up because I’d rather you trust the other three.
Did Regulators Actually Ban the Cloud?
I hear this one constantly, usually as the reason a utility can’t even look at a hosted system. Somebody told them the state won’t allow it.
So let me be straight about what I’ve actually been able to find. There’s no federal rule prohibiting hosted SCADA for water systems. And in the states we work in, I’ve never run into a drinking water agency that bans it either.
What I think happened is that three separate things got blended into one.
A rule that came and went. In March 2023, the EPA told states to start reviewing cybersecurity during routine water system inspections. Several states and two industry associations sued. A federal appeals court put it on hold that July, and the EPA pulled the memo back in October 2023. A lot of operators remember hearing that cybersecurity was about to get inspected, and never heard how it ended.
A requirement that never went away. If you serve more than 3,300 people, the America’s Water Infrastructure Act still requires a risk and resilience assessment and an emergency response plan, and both have to cover your electronic and automated systems. That’s been federal law since 2018. It says nothing about where your software runs.
Guidance that’s about exposure, not hosting. This is the part that gets misread. Every agency publishing on this says the same thing: control equipment shouldn’t be directly reachable from the public internet. WaterISAC lists it second in its twelve cybersecurity fundamentals. NIST covers it. CISA repeats it after every incident. And if you do need remote access, CISA’s guidance is to put a VPN or a gateway device in front of the equipment instead of exposing it.
Read that closely, because “don’t leave your PLC exposed to the internet” is not the same instruction as “don’t use a hosted platform.” One is about what can be reached. The other is about where software runs. They get treated as a single rule, and they aren’t.
One more thing worth sitting with. CISA had updated its advisory about this exact kind of targeting on July 22, 2026, four days before the Minnesota attacks began. The guidance was already out there. Knowing what you’re supposed to do and having a system that makes it easy to do are two different problems.
Think About Your Old Phone System
Before SCADA, I started a phone company, so I’ve watched this happen once already.
Twenty years ago, a business that wanted phones bought a PBX. That meant:
- Owning the server
- Maintaining the hardware
- Installing the software updates
- Adding expansion cards as you grew
- Managing the backups
Today nobody asks what kind of PBX a company owns. They just expect the phones to work.
That didn’t happen because businesses fell in love with the cloud. It happened because a better architecture showed up. I think SCADA is on the same stretch of road. Utilities don’t actually want servers. They want the things SCADA is supposed to deliver: monitoring, alarming, reporting, and control they can count on.
Ask Better Questions
Here’s the part vendors usually skip. Moving to a hosted platform does not make you secure. If someone tells you their system is safe because it runs in the cloud, that’s your cue to ask more questions, not fewer. And when you do move, you’re taking on a vendor. Part of your security now sits with somebody else’s engineering and somebody else’s people. WaterISAC lists third-party risk as one of its twelve fundamentals for a reason.
That’s not an argument against hosted SCADA. It’s an argument for asking vendors harder questions than most of us get asked, and for asking the same questions about the system you already have:
- How many ways are there to reach our control network today?
- How many user accounts are still active for people who left?
- If one device gets compromised, what else can it reach?
- How fast could we shut off remote access in the middle of an incident?
- How many separate pieces of software have to work before somebody can acknowledge an alarm at two in the morning?
AWWA has a free assessment tool that walks a utility through a structured version of this, though you’ll need to make an account. It’s worth an afternoon.
Those answers will tell you more about where you stand than knowing whether your SCADA runs on a server in the back room. And every so often it’s worth asking whether the architecture you’ve built over the past twenty years is still the one you want to defend for the next twenty.
Cloud SCADA Security FAQs
If our internet or cellular connection goes down, do we lose control of the plant?
No. Your PLC keeps running its program either way, because the control logic lives on the controller at your site, not on the platform. Losing a connection affects what you can see and do remotely, not whether the process keeps running. When the connection returns, the hub sends up the readings it recorded while it was offline, so your compliance records stay complete.
Does “no local server” mean equipment leaves the plant?
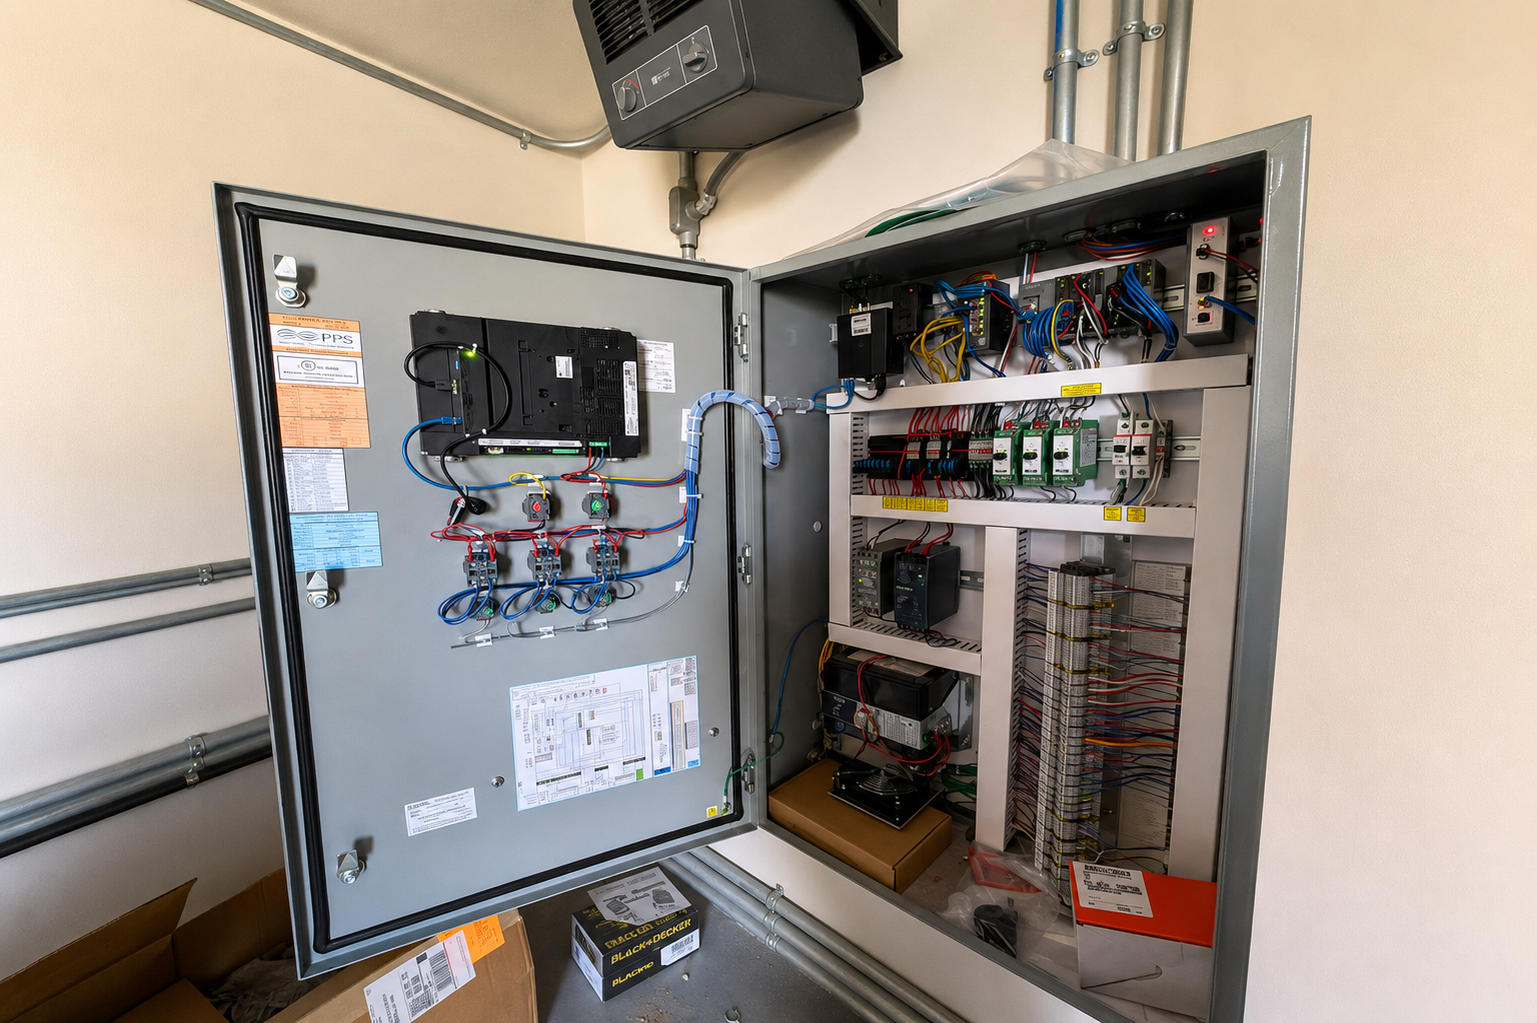
No. Your PLCs, sensors, and control equipment all stay right where they are. What goes away is the PC or server in the back room running the SCADA software, along with the patching, the backups, and the replacement cycle that comes with it. The control still happens on site.
How do we find out whether our own system is exposed to the internet?
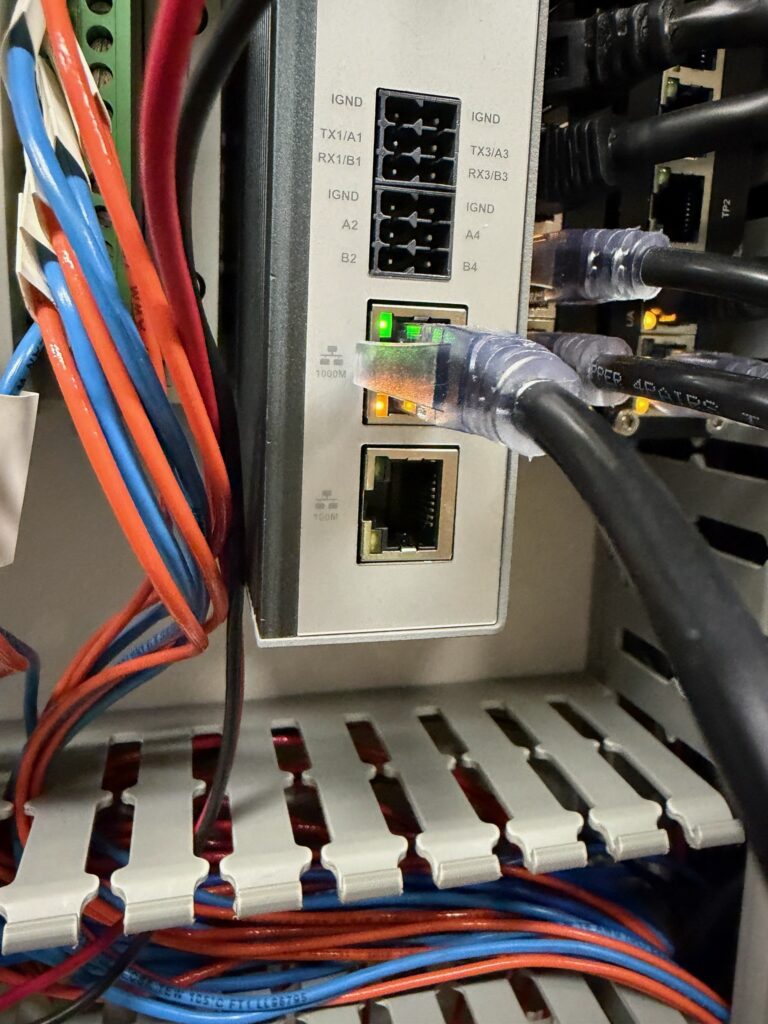
Ask whoever set up your system for a written list of every way to reach your control network from outside: remote logins, vendor access, cellular modems, forwarded ports. Then go down that list and ask who still needs each one. CISA also offers free scanning of internet-accessible assets at no cost, which will flag equipment visible from outside.
Is our data encrypted, and can we require multifactor authentication?
Every device on the system has its own authenticated identity, so the platform knows exactly what’s talking to it. Traffic between your site and the platform is encrypted, and permissions are granular, so each operator sees only what they need and access can be pulled in one place instead of five.
What’s the difference between this and using a VPN?
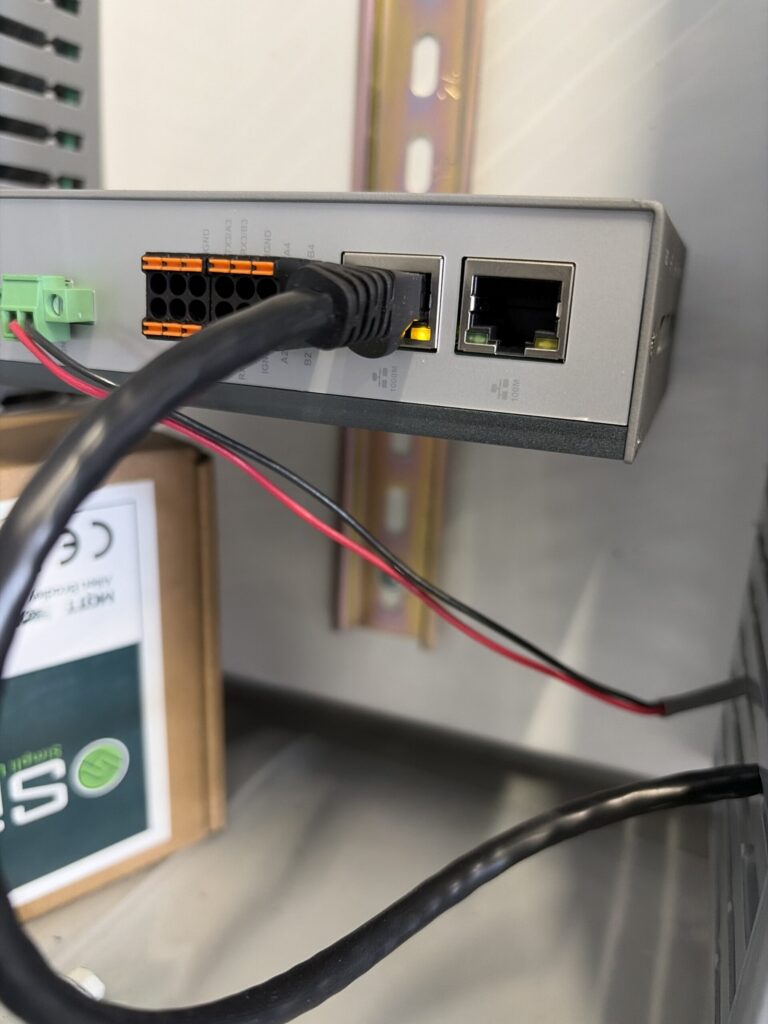
A VPN builds an encrypted tunnel into your network, so remote users reach your equipment through a locked entrance instead of an open one. CISA recommends it and it works. The difference is that a VPN protects a pathway into the plant. An outbound-only setup doesn’t create one. Both reduce exposure. One leaves you less to maintain.
Book a Free Demo

If you want to map out your own pathways with somebody, that’s a conversation I’m always glad to have. Book a free demo and we’ll walk through your actual water or wastewater setup instead of a slide deck. Or if you’d rather poke at it yourself first, there’s a 90-day trial.